
LangSmith BYOC 现已在 AWS、Azure 和 Google Cloud 上推出
原题LangSmith BYOC is now available on AWS, Azure, and Google Cloud
推荐理由LangSmith BYOC 跨三云提供客户账户内的数据和部署控制,为企业比较托管便利性与私有网络边界提供具体选项。
读前速览
LangSmith 自带云(BYOC)现已在 AWS 上正式推出,并在 Azure 和 Google Cloud 上进入 Beta 阶段,让组织能够将追踪记录、评估、数据集和智能体部署保留在自己的云账户中,同时由 LangChain 管理控制平面和基础设施。
BYOC 架构将控制平面与数据平面分离
组织可以在所选云账户中保有数据平面的所有权,而 LangChain 负责管理控制平面,包括身份验证、计费和 UI 资源,从而确保合规性和数据主权。
针对 AWS、Azure 和 Google Cloud 的云平台特定实现
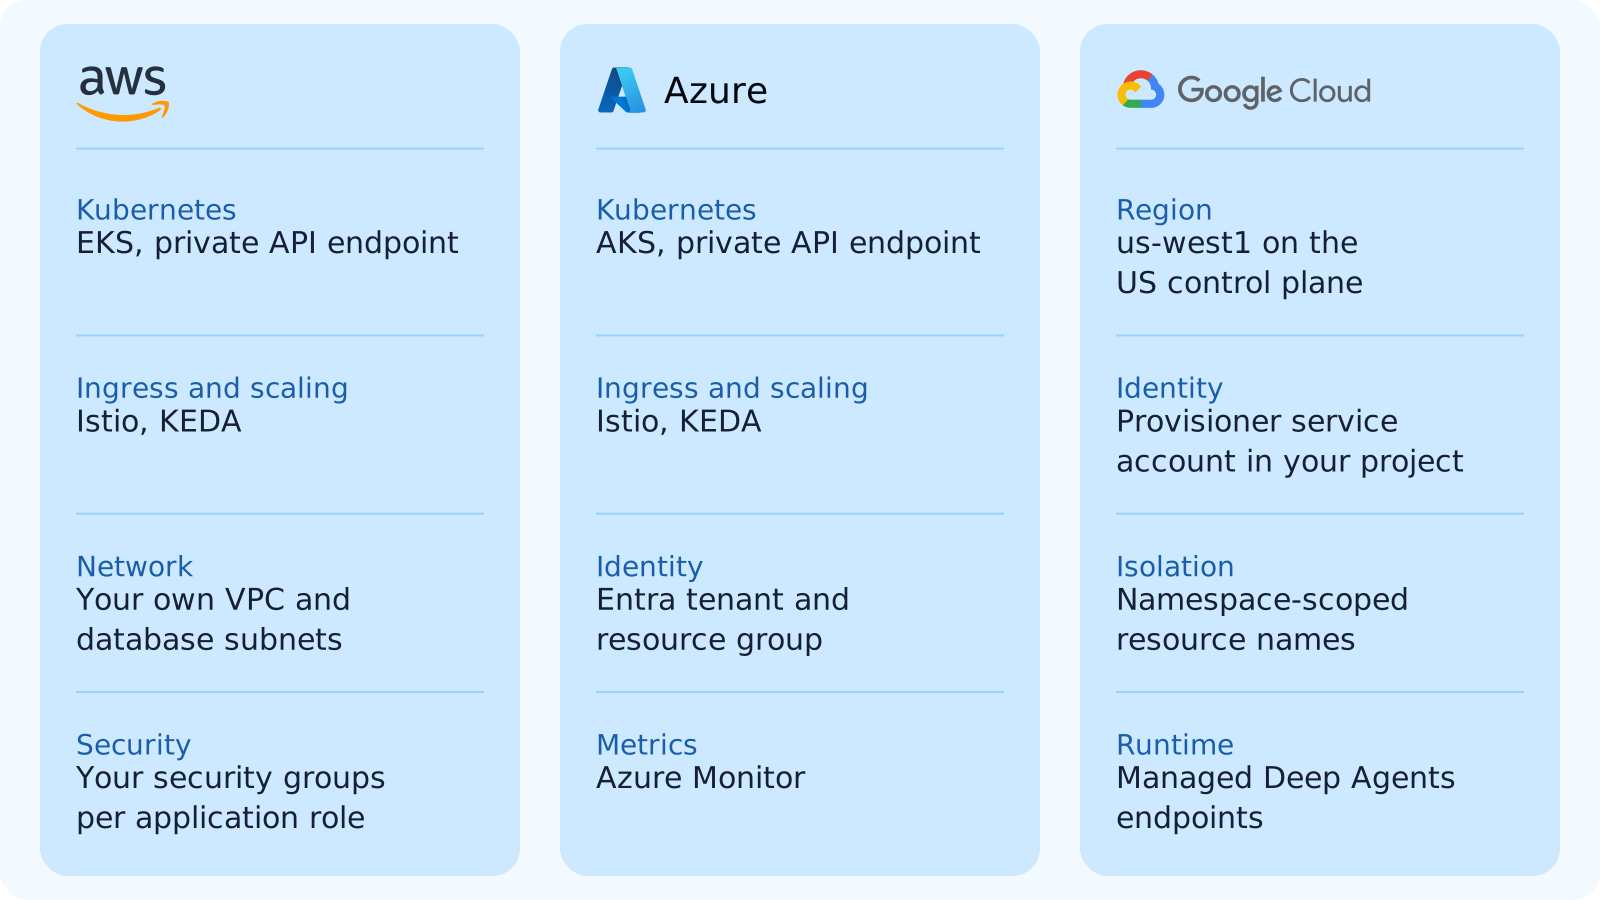
各云平台采用原生构建模块:AWS 在现有 VPC 内运行,并支持自定义安全组;Azure 使用带有 Istio 和 KEDA 的专用 AKS;Google Cloud 则支持多区域部署,并使用命名空间级别的资源。
支持从自托管环境迁移至 BYOC
开源迁移工具可迁移工作区、数据集、实验、提示词和 Fleet 资源;LangChain 负责迁移追踪记录(目前已在 AWS 上提供),并在不中断服务的情况下保留现有数据。
持续升级和自动扩缩容等优势
团队无需安排维护窗口或执行 Helm 升级;新功能可以快速部署到 BYOC 数据平面,服务也会根据负载自动扩缩容,从而保持稳定运行时间。
完整摘要
LangSmith BYOC 将平台划分为由 LangChain 管理的控制平面,以及由客户在所选云平台上拥有的数据平面(AWS 正式推出,Azure 和 Google Cloud 处于 Beta 阶段)。数据平面会在客户的 VPC 或账户中存储所有敏感信息,包括追踪记录、提示词、数据集、实验和智能体部署;LangChain 则负责编排、扩缩容和更新。这样既免去了自托管部署的维护负担,也能实现持续升级、自动扩缩容,并更快获取新功能。迁移工具支持将现有自托管资源和追踪记录迁移至 BYOC。Terraform 模块和迁移工具均为开源项目;LLM Gateway 支持 11 家服务提供商,以及兼容 OpenAI 和 Anthropic 的端点。
目录 · 7 节
LangSmith 自带云(BYOC)现已支持在 AWS 上运行(正式发布),并支持在 Azure(Beta 版)和 Google Cloud(Beta 版)上运行。您的追踪记录、评估、数据集、提示词和智能体部署都保留在您自己的云账户中,由您选择云平台;LangChain 则为您管理数据平面,涵盖编排、扩缩容和平台更新。LangSmith Bring Your Own Cloud (BYOC) now runs on AWS (GA), Azure (Beta), and Google Cloud (Beta). Your traces, evals, datasets, prompts, and agent deployments stay in your own cloud account, on the cloud you choose, and LangChain manages the data plane for you, from orchestration and scaling to platform updates.
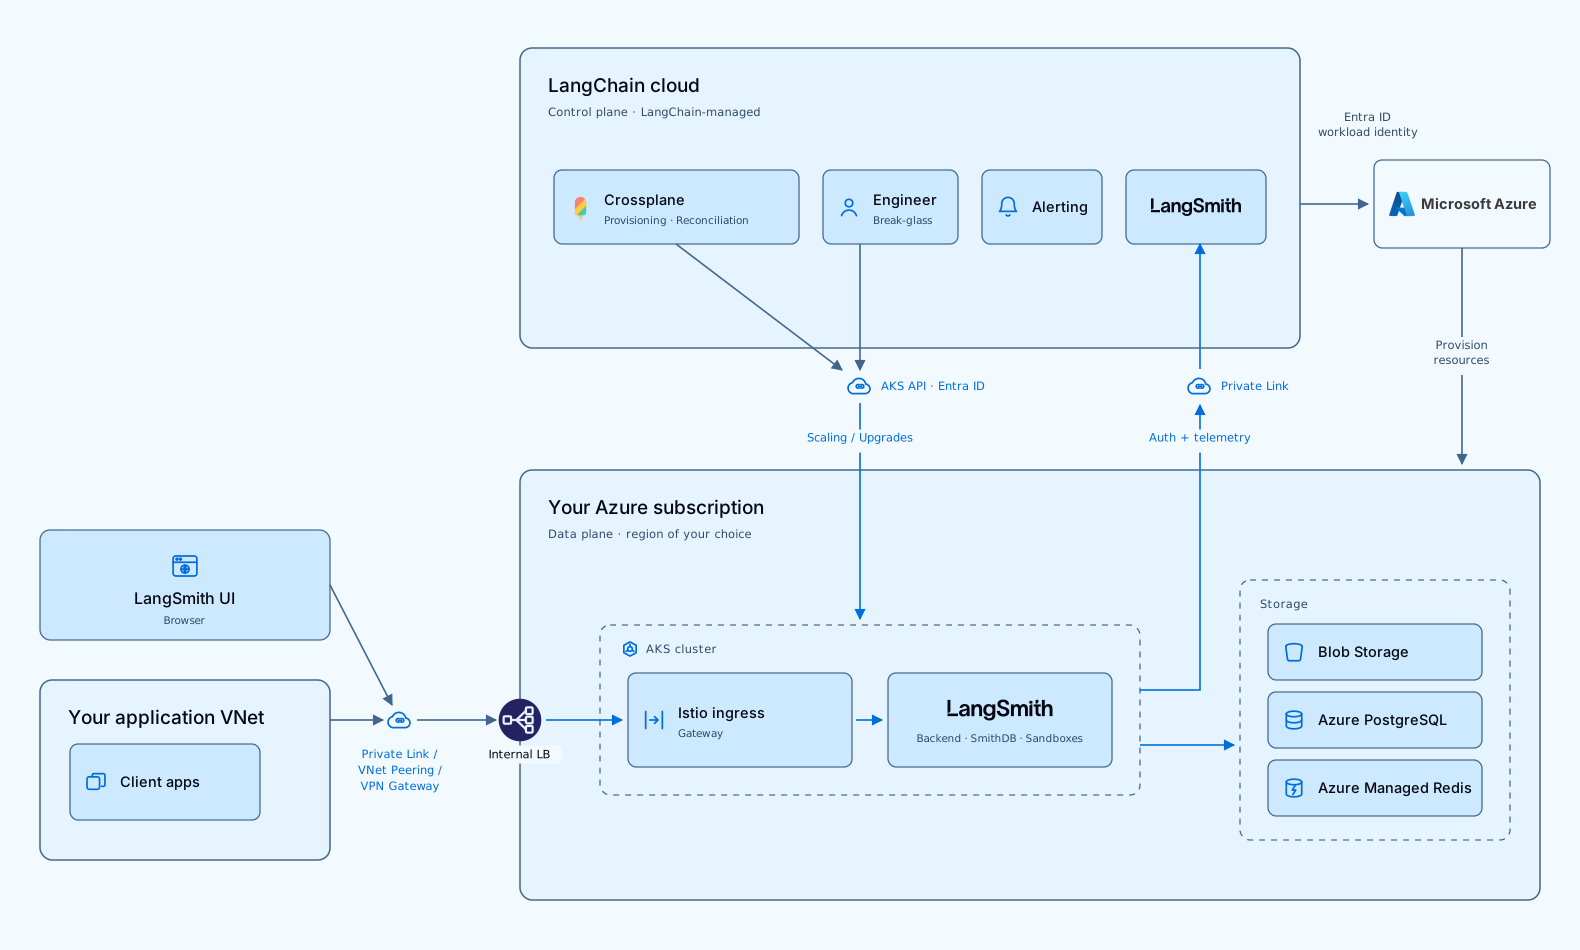
BYOC 如何拆分 LangSmithHow BYOC splits LangSmith
你可以自行决定代理运行在哪里、遥测数据存储在哪里,而无需承担自行运行 LangSmith 的工作。为此,BYOC 将 LangSmith 拆分为两部分。LangChain 负责运行控制平面,其中包含身份验证、组织和工作区配置、账单元数据、哈希后的 API 密钥以及静态 UI 资源。你拥有数据平面,其中存储所有敏感信息,从追踪记录、提示词和数据集,到实验、代理部署和工作区密钥。You decide where your agents run and where your telemetry lives, without taking on the work of running LangSmith yourself. To make that possible, BYOC splits LangSmith in two. LangChain runs the control plane, which holds auth, org and workspace config, billing metadata, hashed API keys, and static UI assets. You own the data plane, which holds everything sensitive, from traces, prompts, and datasets to experiments, agent deployments, and workspace secrets.

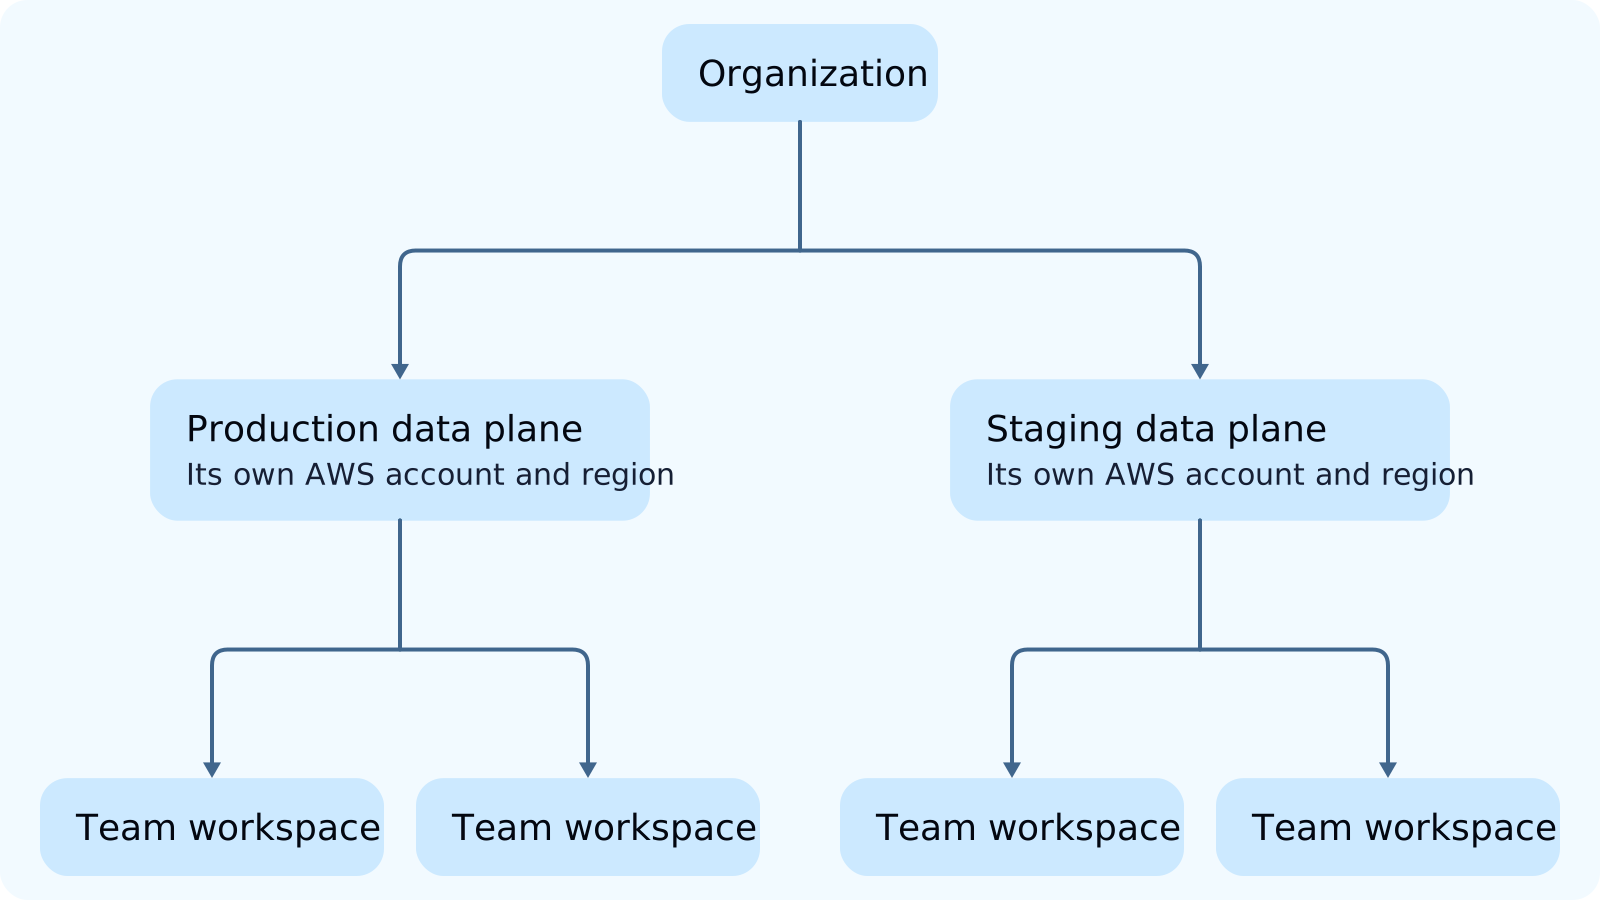
一个组织可以拥有多个数据平面,每个数据平面位于各自的账户和区域中,并包含其工作区。这样,您就可以按区域、环境或业务部门拆分数据平面。An organization can hold several data planes, each in its specific account and region, and each data plane holds its workspaces. This lets you split data planes by region, environment, or business unit.
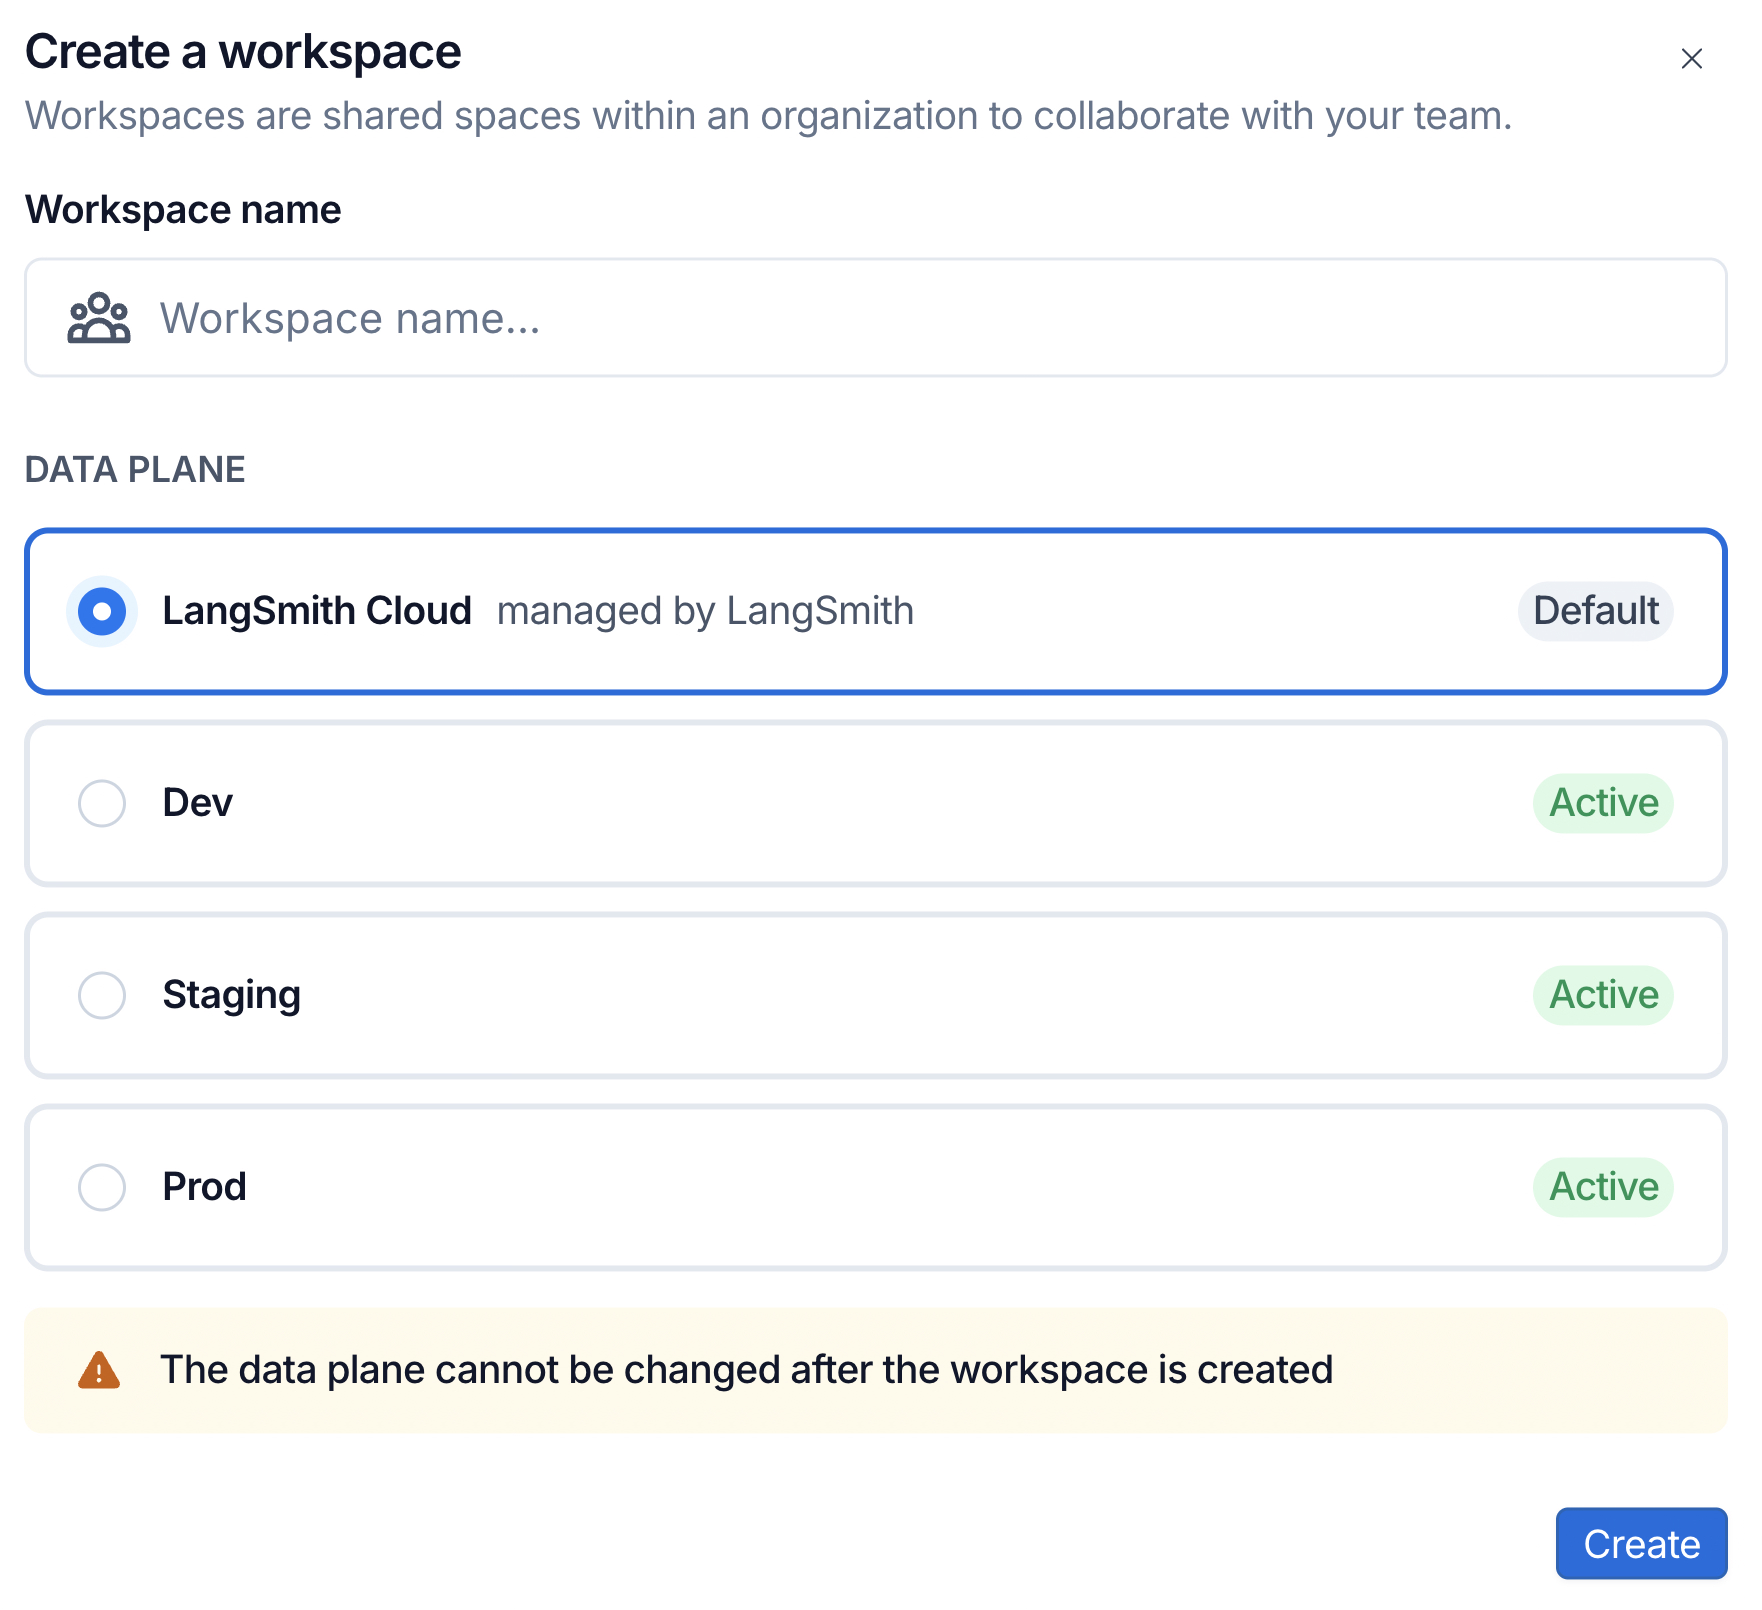
例如,平台团队可能会在不同的 AWS 账户中运行生产和预发布数据平面,而一个已将 Azure 作为标准平台的业务部门,则会在 Azure 上运行自己的独立 BYOC 部署。每个团队的追踪数据都会进入该团队拥有的账户。For example, a platform team might run production and staging data planes in separate AWS accounts, while a business unit that standardized on Azure runs its own, separate BYOC deployment on Azure. Each team's traces land in the account that team owns.
我们为什么构建 BYOCWhy we built BYOC
此前,受严格合规边界限制的团队会部署并维护自托管的 LangSmith。这样可以确保数据留在自身边界内,但需要专职的平台工程师来为有状态服务打补丁、配置数据库并执行架构迁移。Until now, teams with strict compliance boundaries deployed and maintained self-hosted LangSmith. This kept their data inside their own boundary, but it took dedicated platform engineers to patch stateful services, configure databases, and run schema migrations.
通过 BYOC,LangChain 会在你自己的虚拟网络中部署并运行 LangSmith。假设有一个团队在多个环境中运行智能体应用。采用自托管时,每次更新执行组件都意味着要协调停机,并在各个环境中管理自定义的 Helm 部署流程。采用 BYOC 时,数据平面中的数据会保留在你的 VPC 中,而 LangChain 负责处理扩缩容、架构更新和运行时依赖项。With BYOC, LangChain provisions and operates LangSmith inside your own virtual network. Consider a team running agent applications across several environments. With self-hosted, every update to the execution components meant coordinating downtime and managing custom Helm rollouts in each environment. With BYOC, the data in your data plane stays in your VPC while LangChain handles scaling, schema updates, and runtime dependencies.
AWS 客户的所见所闻What AWS customers have seen
自 8 月在 AWS 上推出 BYOC 以来,许多团队选择通过 BYOC 在自己的云环境中运行 LangSmith。他们指出了三大主要优势:Since we launched BYOC on AWS in August, many teams have chosen to run LangSmith in their own cloud with BYOC. They point to three main benefits:
- 持续升级。LangChain 会持续推出平台更新,因此团队无需再安排维护窗口或管理 Helm 升级。Continuous upgrades. LangChain rolls out platform updates, so teams no longer plan maintenance windows or manage Helm upgrades.
- 最新的 LangSmith 功能。新功能在 LangSmith Cloud 上线后不久就会登陆 BYOC 数据平面,无需等待下一次自托管版本发布。The latest LangSmith features. New features reach BYOC data planes soon after they ship on LangSmith Cloud, without waiting for the next self-hosted release.
- 自动扩缩容。服务会随负载变化进行扩缩容,因此随着使用量增长,团队仍能获得稳定的正常运行时间和流畅的体验。Automatic scaling. Services scale with load, so teams get consistent uptime and a smooth experience as usage grows.
正是出于这一需求,我们迅速将 BYOC 引入 Azure 和 Google Cloud,让团队无论使用哪种云,都能获得同样的体验。That demand is why we moved quickly to bring BYOC to Azure and Google Cloud, so teams can get access to this same experience on whichever cloud they run.
BYOC 在各个云平台上的表现形式What BYOC looks like on each cloud
每个云都有自己的网络策略、身份模型和安全要求,因此 BYOC 基于各云自身的构建模块搭建。在这三种云上,BYOC 数据平面也会运行 Managed Deep Agents 端点。Each cloud has its own network policies, identity model, and security requirements, so BYOC is built from each cloud's own building blocks. On all three clouds, BYOC data planes also run Managed Deep Agents endpoints.
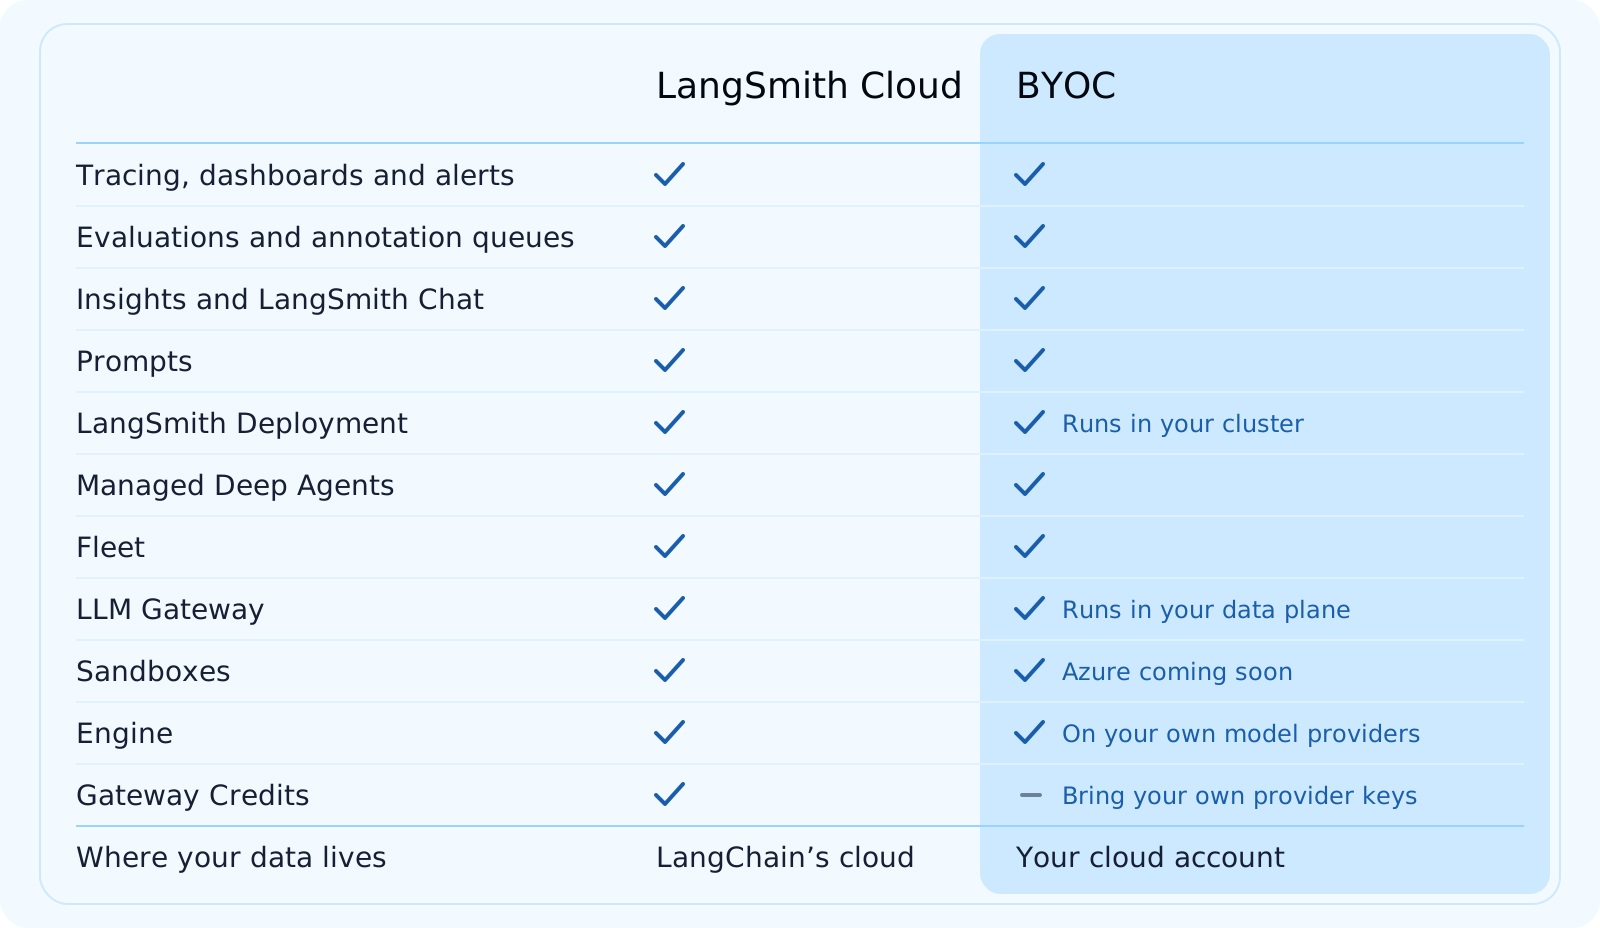
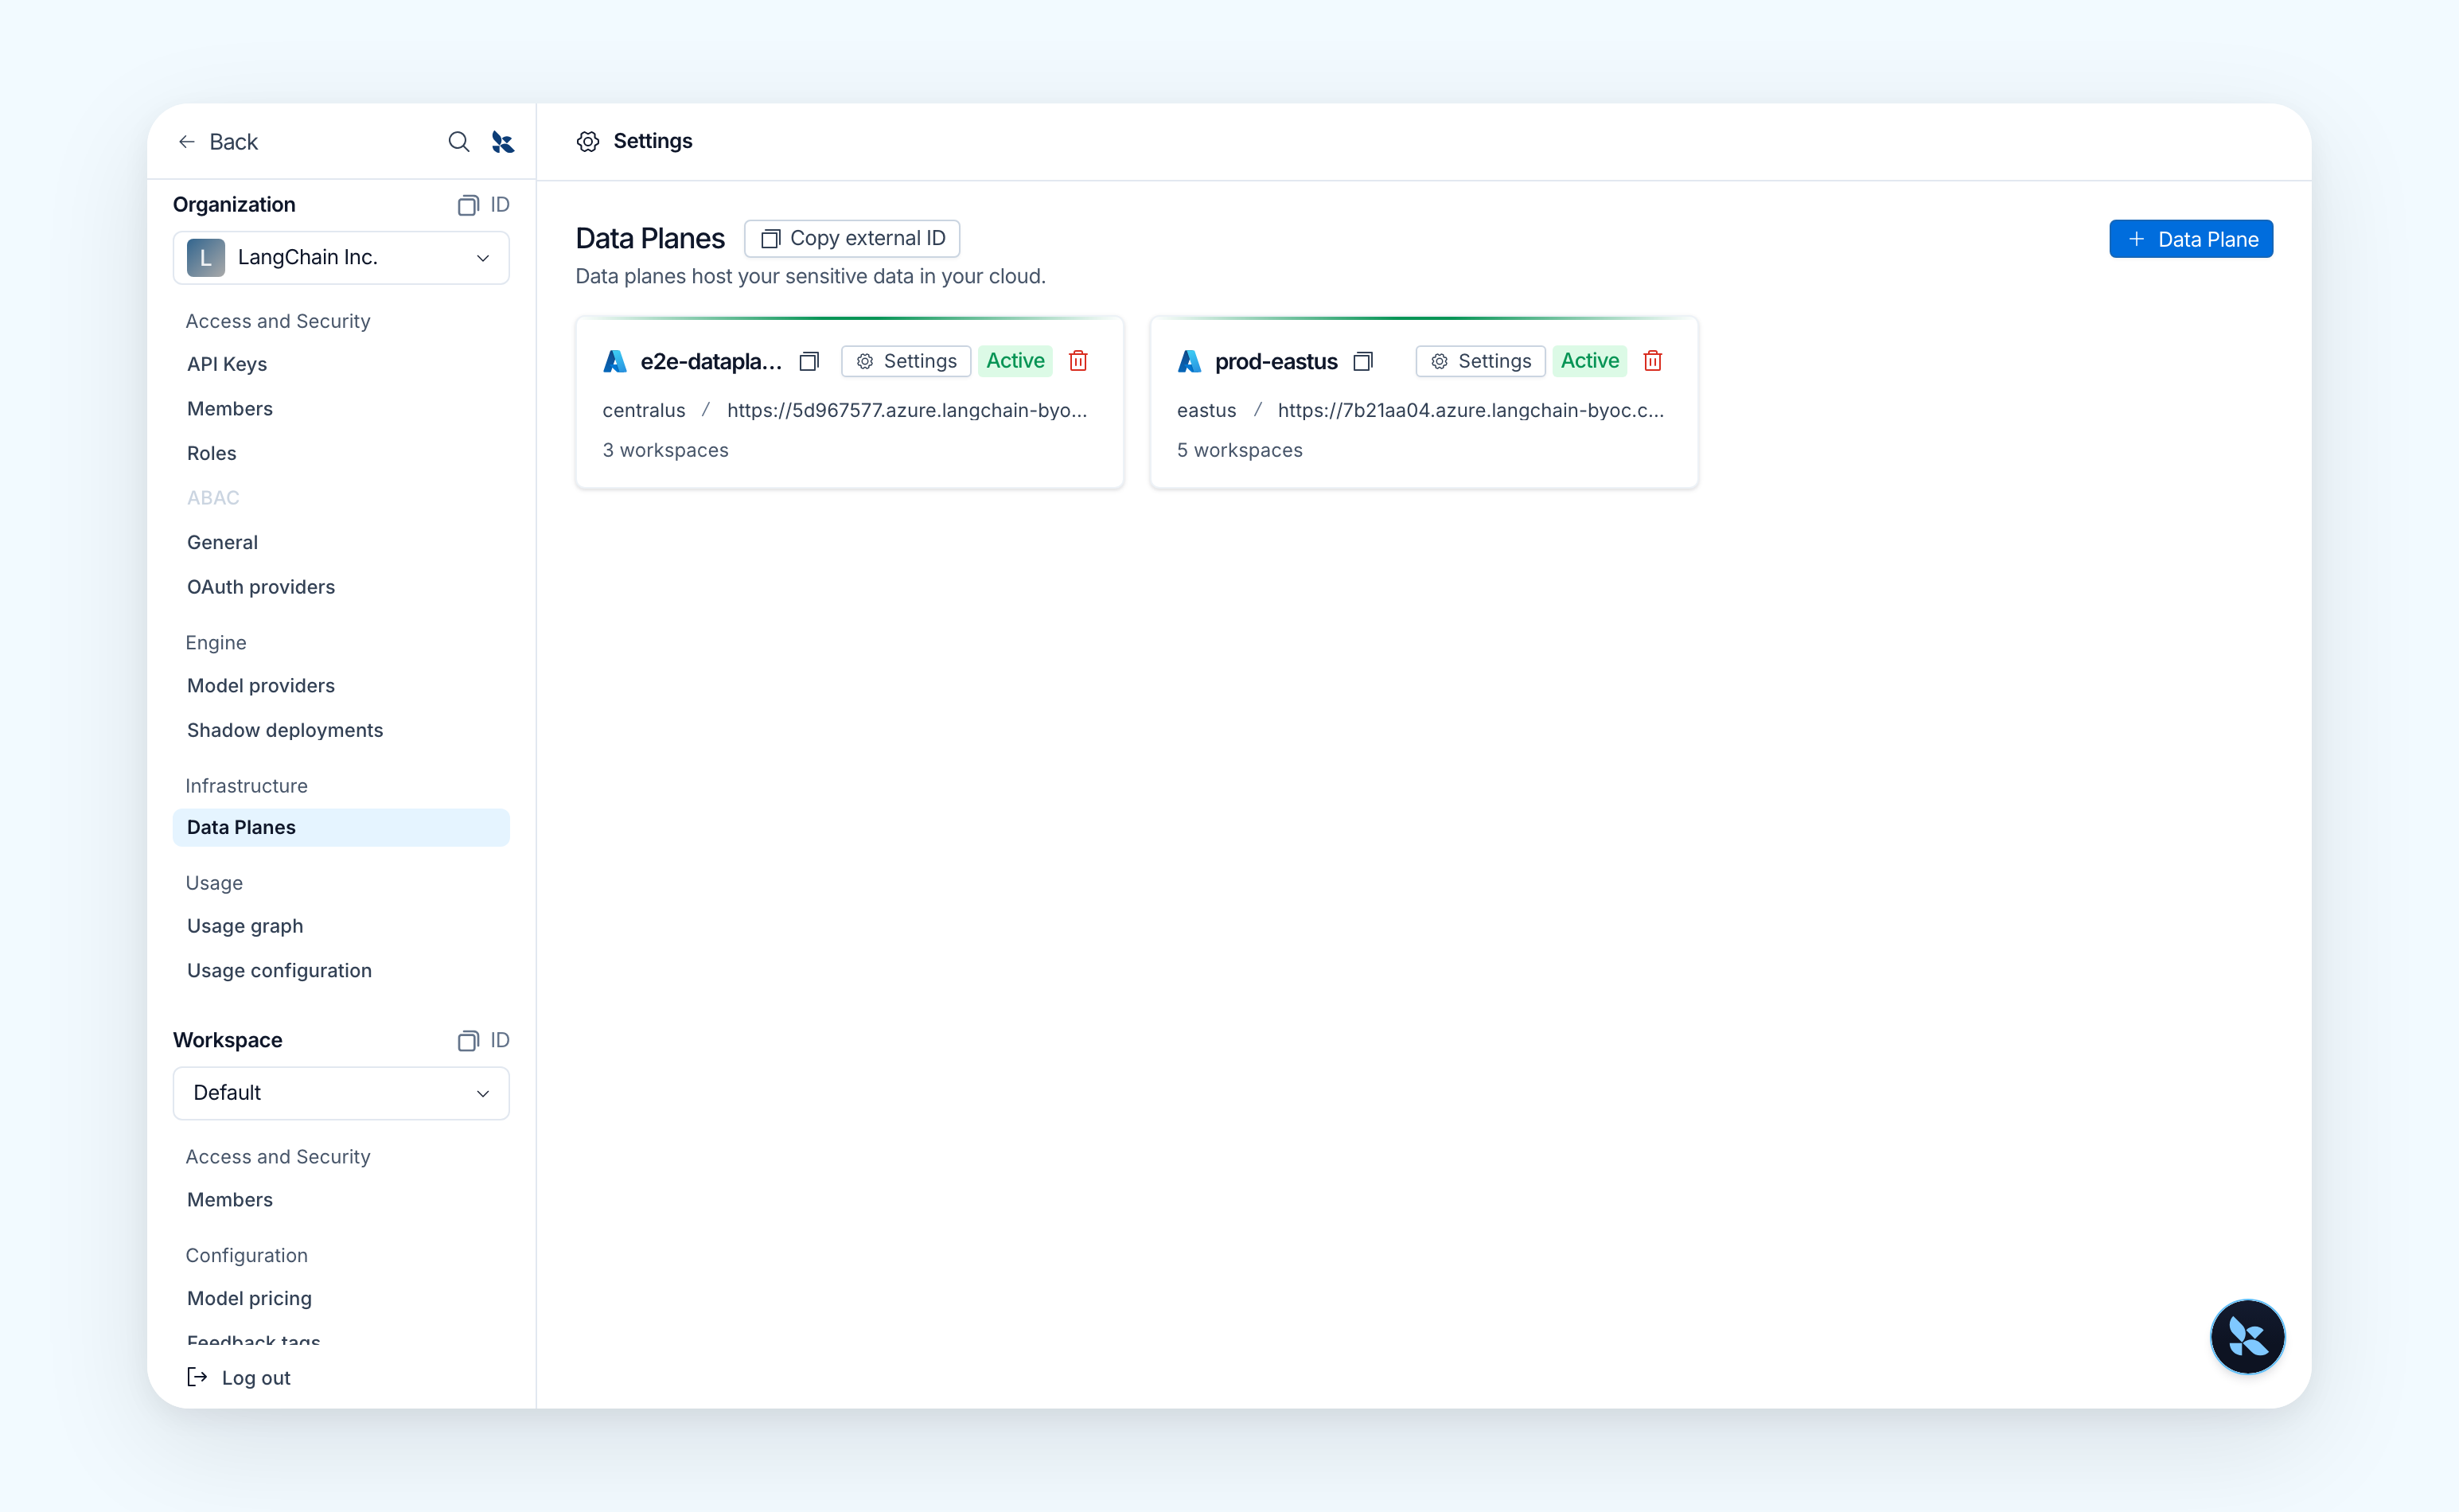
Azure:BYOC 会在专用虚拟网络内运行数据平面,并使用私有 AKS API 端点。我们通过 Helm 部署 Istio 和 KEDA,以实现入口流量路由和事件驱动的扩缩容;系统遥测数据则发送到 Azure Monitor。Azure 上的 LangSmith Sandboxes 支持即将推出。Azure: BYOC runs the data plane inside a dedicated virtual network with a private AKS API endpoint. We deploy Istio and KEDA with Helm for ingress routing and event-driven scaling, and system telemetry goes to Azure Monitor. Support for LangSmith Sandboxes on Azure is coming soon.
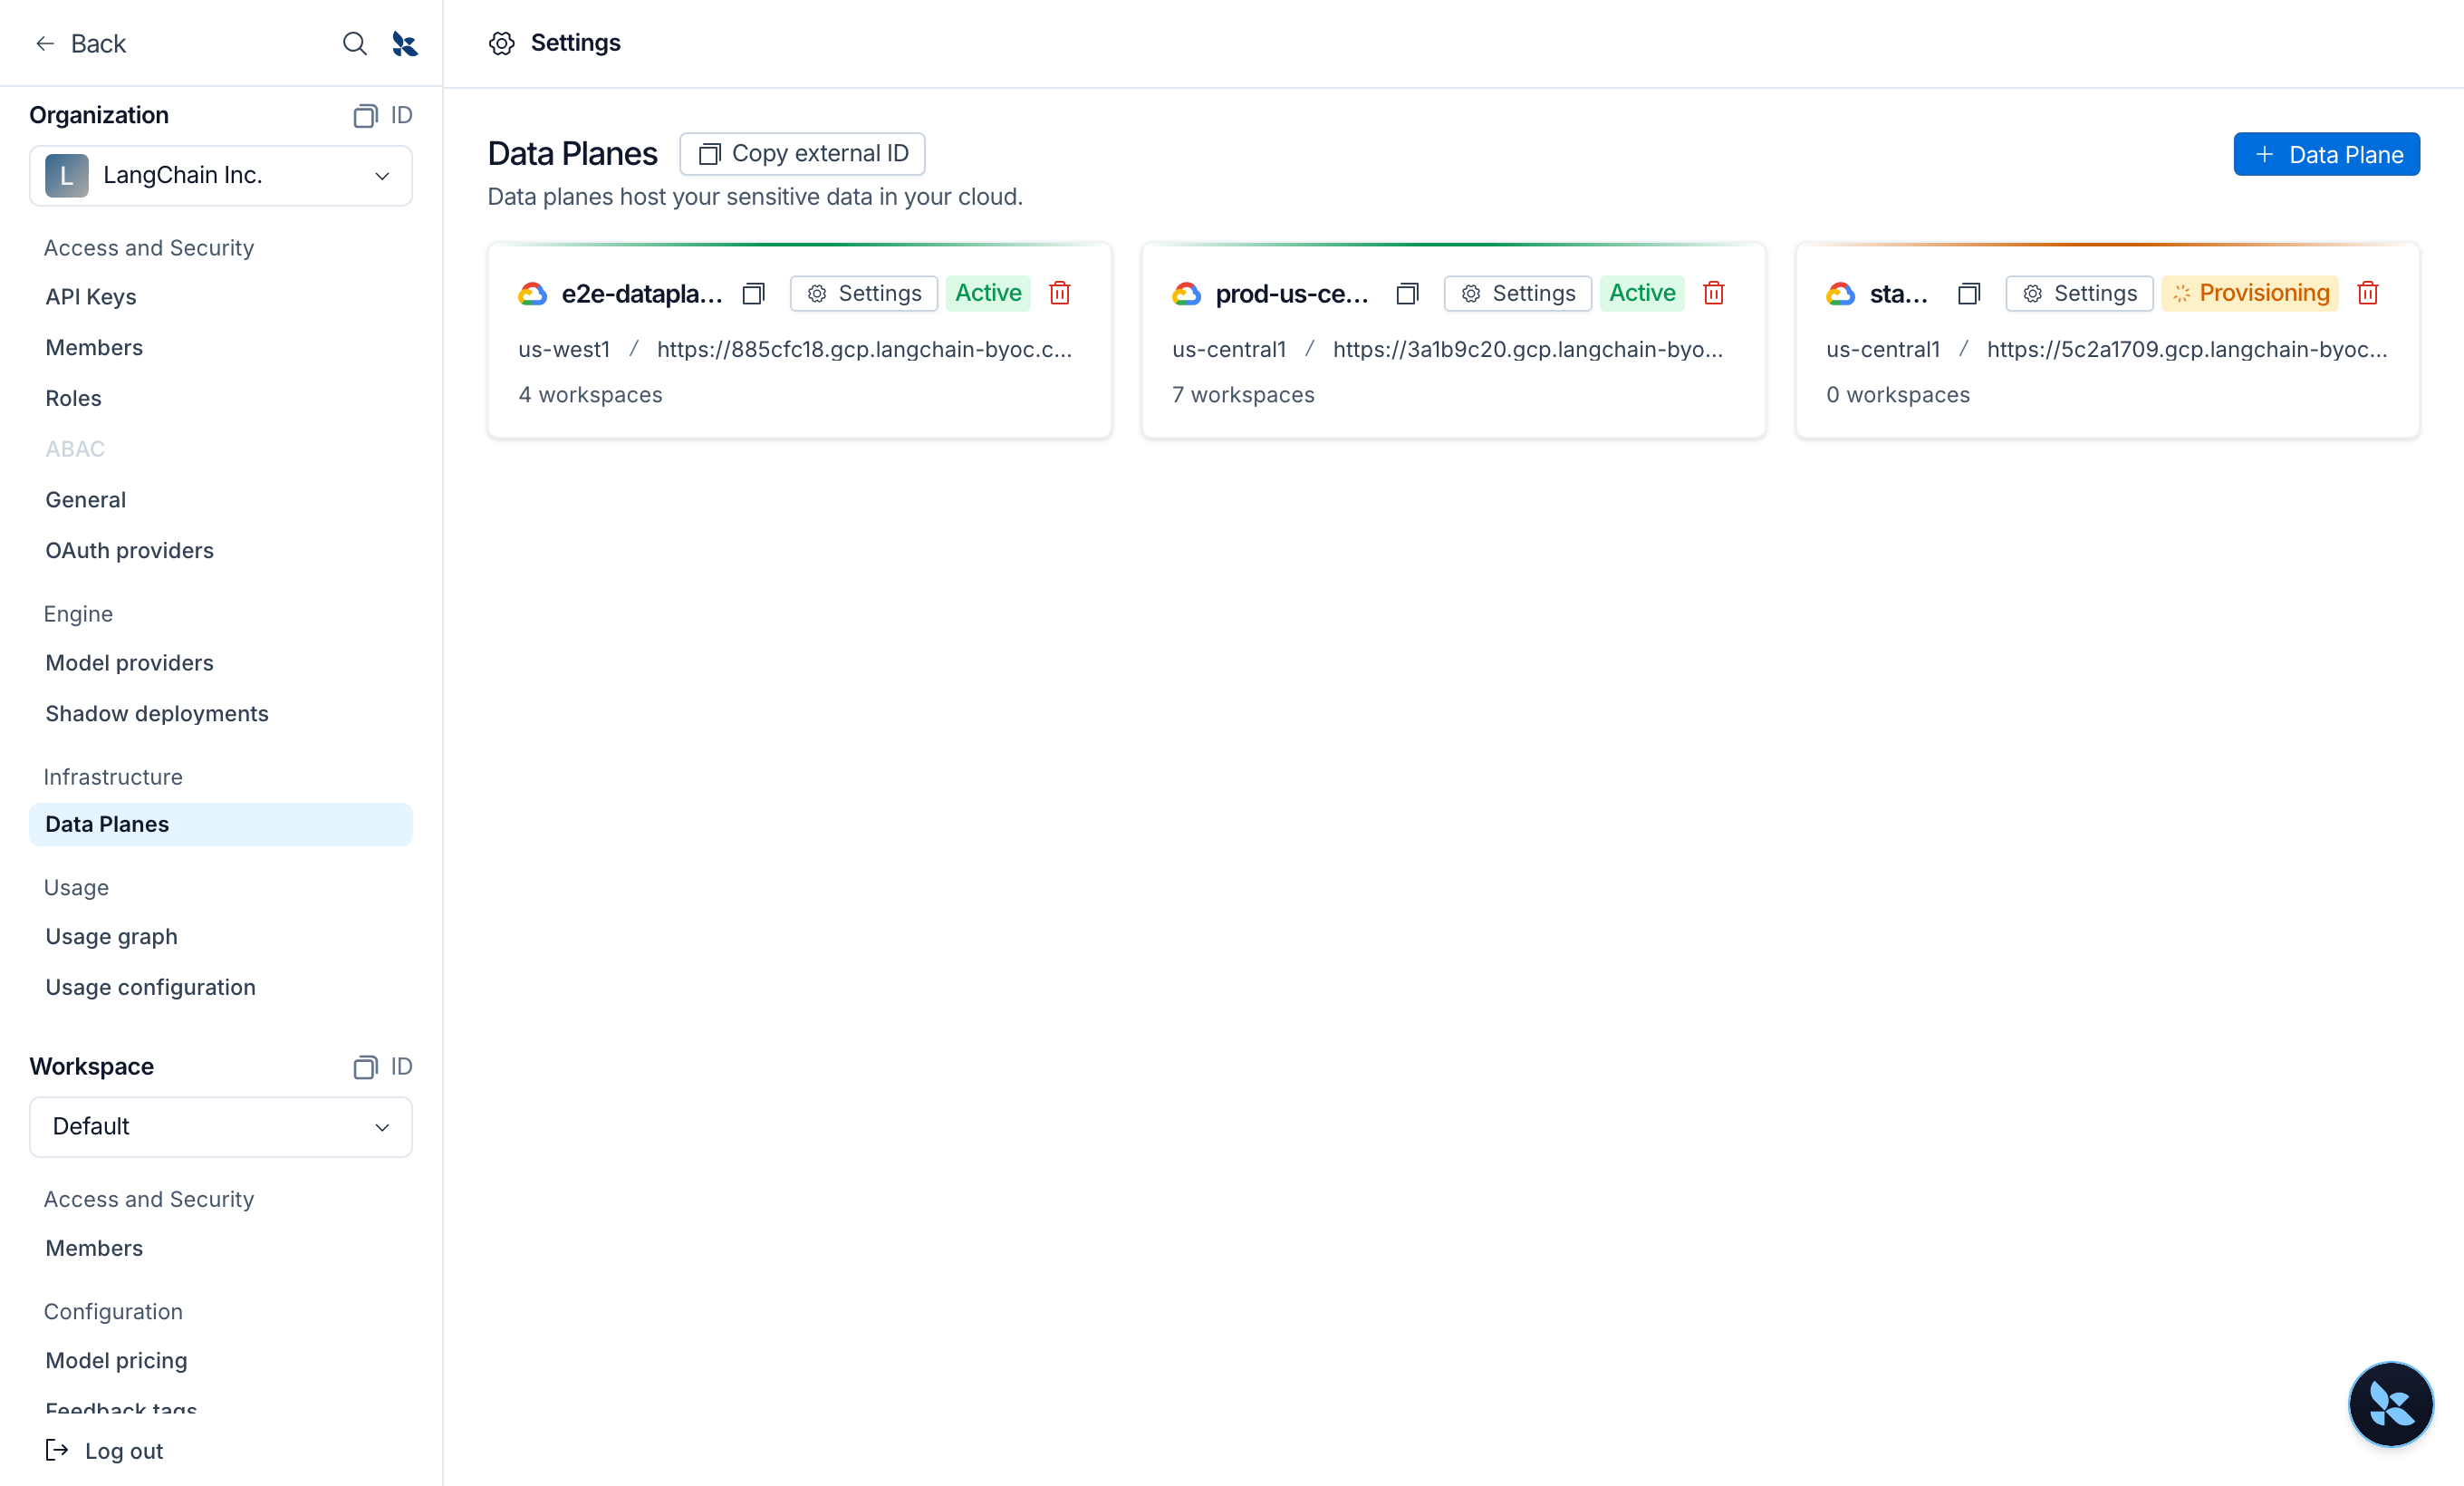
Google Cloud:发布时,Google Cloud 数据平面可以在任何区域运行,并由 LangSmith 的美国控制平面管理。资源使用限定于命名空间的名称,因此不会与您现有的基础设施冲突。Google Cloud: At launch, Google Cloud data planes can run in any region and are managed from LangSmith's US control plane. Resources use namespace-scoped names, so they don't collide with your existing infrastructure.
AWS:BYOC 在您现有的 VPC 内运行,数据库位于您选择的子网中。安全团队可以为每个应用角色附加自己的安全组,使数据平面符合您现有的入站和出站流量检查策略。AWS: BYOC runs inside your existing VPC, with the database in subnets you choose. Security teams can attach their own security groups to each application role, so the data plane fits the ingress and egress inspection policies you already run.
无需从头开始,即可从自托管版本迁移出去Move from self-hosted without starting over
自托管 LangSmith 让你完全掌控数据的存储位置,但需要投入大量维护工作。BYOC 会将数据保留在你的账户中,同时由我们负责运行基础设施;你也可以将现有的自托管数据一并迁移过来。Self-hosted LangSmith gave you full control of where your data lives, but required significant maintenance overhead. BYOC keeps the data in your account while we run the infrastructure, and you can bring your existing self-hosted data with you.
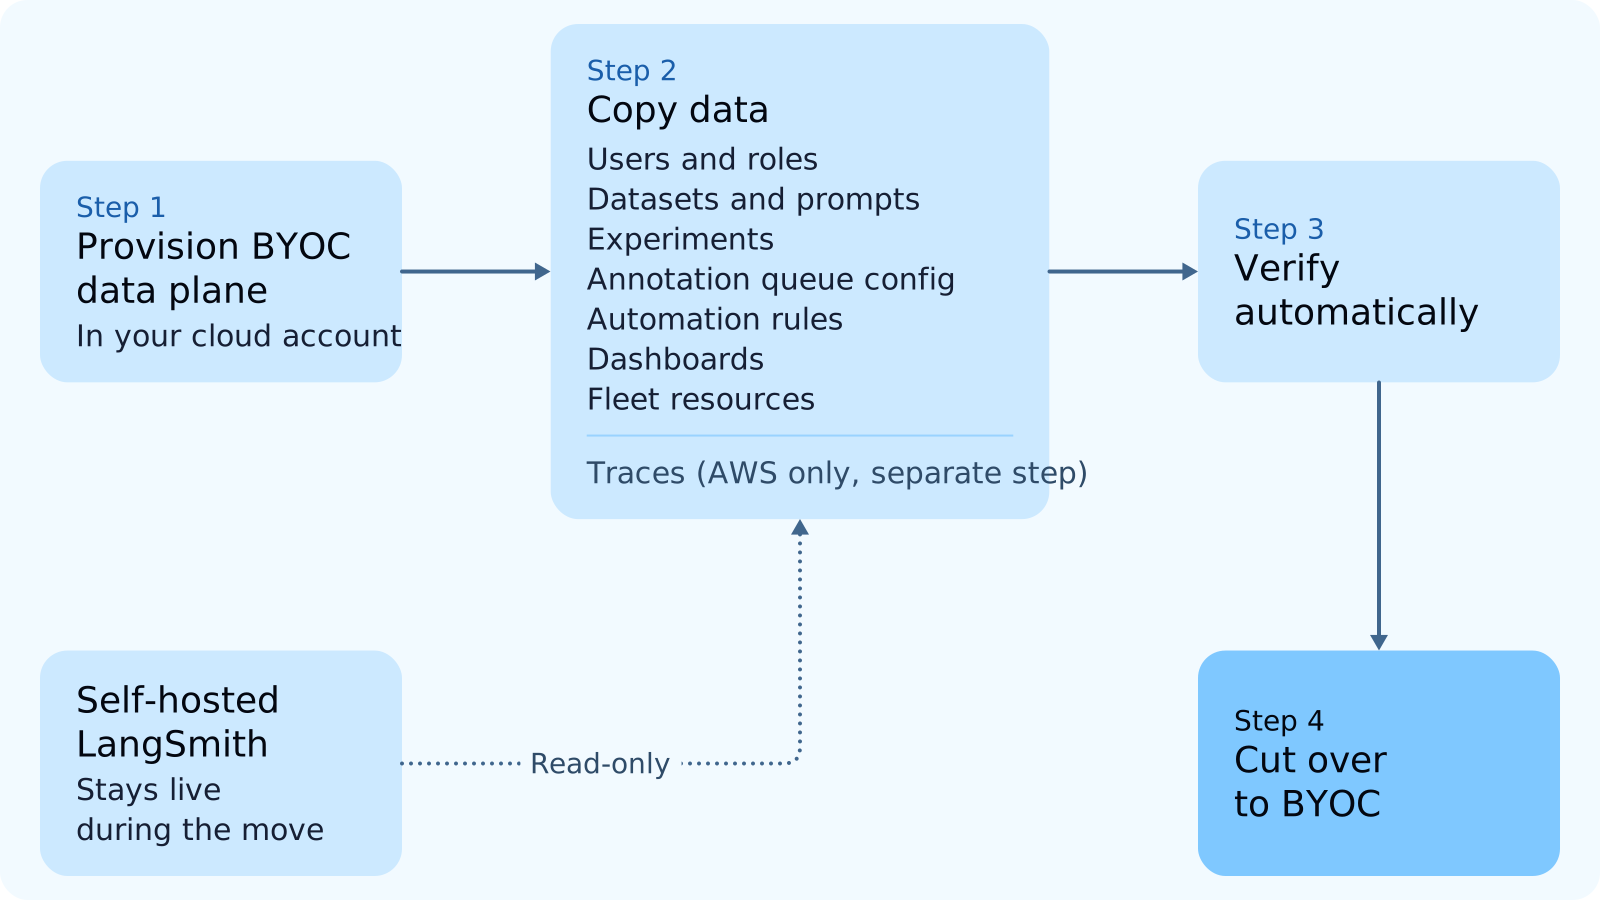
迁移分为两部分。工作区资源会通过我们的开源迁移工具迁移;该工具从您自托管的实例读取数据,迁移期间不会对其进行更改,实例也会继续正常运行。在所有云环境中,它都会迁移用户和角色、数据集、实验及提示词。此外,它还会迁移标注队列配置、自动化规则、仪表板和 Fleet 资源。The move has two parts. Your workspace resources move with our open source migration tool, which reads from your self-hosted instance and leaves it untouched and live during the move. On every cloud, it covers users and roles, datasets, experiments, and prompts. It also brings over annotation queue config, automation rules, dashboards, and Fleet resources.
您的追踪记录、运行记录和反馈会作为一个独立步骤进行迁移,该步骤由 LangChain 使用内部工具为您执行。目前,AWS 上已支持追踪记录迁移。Your traces, runs, and feedback move as a separate step that LangChain runs for you with internal tooling. Trace migration is available on AWS today.
开源与公共 TerraformOpen source and public Terraform
LangChain 和 LangGraph 均为开源项目。BYOC 背后的 Terraform 模块和迁移工具都公开托管在 github.com/langchain-ai/terraform。数据平面中的 LLM Gateway 开箱即用即可调用 11 家提供商的模型,以及任何兼容 OpenAI 或 Anthropic 的端点,因此你既可以选择其背后的模型提供商,也可以选择云平台。LangChain and LangGraph are open source. The Terraform modules behind BYOC are public at github.com/langchain-ai/terraform, and so is the migration tool. The LLM Gateway on your data plane calls models from 11 providers out of the box, plus any OpenAI- or Anthropic-compatible endpoint, so you choose the model provider behind it as well as the cloud.
开始使用Get started
联系销售团队,在 AWS、Azure 或 Google Cloud 上开通 BYOC 数据平面。文档涵盖架构、共同责任模型、迁移、使用方法以及常见问题解答,API 参考中则包含 Create Data Plane API。Contact sales to provision a BYOC data plane on AWS, Azure, or Google Cloud. The docs cover the architecture, the shared responsibility model, migration, usage, and common questions in the FAQ, with the Create Data Plane API in the API reference.